Https //Tinyurl.com Mastering HTTPS Security and Efficiency
Table of Contents
- Technical Breakdown of TinyURL’s HTTPS Implementation and URL Shortening Process
- HTTPS Role in TinyURL’s URL Shortening Pipeline
- Cryptographic Protocols and TLS/SSL Configuration in TinyURL
- HTTP Request/Response Cycle for TinyURL Redirects
- Comparison of HTTPS Implementations: TinyURL vs. Bit.ly vs. Rebrandly
- Use Cases and Functional Applications of TinyURL with HTTPS
- Industry-Specific Applications of HTTPS-Enabled TinyURLs
- Critical Real-World Applications of HTTPS-Enabled TinyURLs
- Security Risks and Mitigation Strategies for HTTPS TinyURLs
- Five Common Vulnerabilities in HTTPS TinyURL Implementations
- Comparison of TinyURL’s Security Measures vs. Open-Source Alternatives
- A Performance Optimization for HTTPS TinyURL Redirects HTTPS TinyURL redirects rely on low-latency resolution to maintain user experience and SEO integrity. Optimization strategies focus on reducing Time-to-First-Byte (TTFB) and connection overhead while ensuring scalability. Server-side caching, protocol efficiency, and resource preloading are critical levers for achieving sub-100ms redirect times, even under high traffic loads. This section examines technical implementations, trade-offs, and measurable improvements in HTTPS redirect performance. Server-Side Caching and CDN Integration for HTTPS Redirects
- HTTP/2 vs. HTTP/3 for TinyURL Redirects: Protocol Trade-offs
- Optimization Techniques for HTTPS Redirects: Trade-offs and Speed Gains
The integration of HTTPS within URL shortening services like TinyURL represents a critical convergence of security and functionality in modern digital ecosystems. As shortened links permeate marketing, cybersecurity, and enterprise communications, the cryptographic backbone of HTTPS ensures data integrity, authenticity, and confidentiality during redirects. Beyond basic encryption, TinyURL’s HTTPS implementation addresses nuanced challenges—from certificate validation to mixed-content handling—while optimizing performance for global audiences. This analysis dissects the technical underpinnings, real-world applications, and security risks of HTTPS TinyURLs, alongside actionable strategies to mitigate vulnerabilities and enhance redirect efficiency.
From compliance with GDPR to preventing phishing attacks, HTTPS TinyURLs serve as silent guardians of digital trust. Yet, their potential remains underleveraged in niche sectors like IoT or legal document sharing, where secure redirects could redefine workflows. By examining protocol trade-offs, server-side optimizations, and auditing techniques, this exploration equips stakeholders to harness TinyURL’s HTTPS capabilities with precision and foresight.
Technical Breakdown of TinyURL’s HTTPS Implementation and URL Shortening Process
The HTTPS protocol underpins TinyURL’s URL shortening service by ensuring secure, encrypted communication between users and servers. This integration is critical for protecting sensitive data during link creation, sharing, and redirection while validating domain authenticity through cryptographic protocols. TinyURL’s infrastructure leverages TLS/SSL to encrypt traffic, mitigate mixed-content warnings, and enforce HTTPS compliance across redirects, distinguishing it from competitors like Bit.ly and Rebrandly in terms of security rigor and performance optimization.The role of HTTPS in TinyURL extends beyond basic encryption; it enforces domain validation, prevents man-in-the-middle attacks, and ensures compliance with modern web standards. Cryptographic protocols such as TLS 1.2/1.3 are employed to establish secure sessions, while certificate authorities (e.g., Let’s Encrypt, DigiCert) authenticate TinyURL’s domain ownership. Redirects are handled via HTTP status codes (301/302) with strict HTTPS enforcement, even in edge cases like legacy HTTP links or third-party integrations.
HTTPS Role in TinyURL’s URL Shortening Pipeline
TinyURL’s HTTPS implementation functions at three critical stages: link creation, storage, and redirection. During creation, users submit a target URL via an HTTPS endpoint, where the server validates the input, generates a shortened alias, and stores the mapping in a secure database. The redirection process relies on TLS to encrypt the alias-to-target resolution, ensuring that neither the shortened link nor the final destination is exposed in plaintext.Key HTTPS contributions include:
TinyURL’s architecture prioritizes HTTPS by default, even for internal redirects. For example, when a user clicks `tinyurl.com/abc123`, the server responds with a 301 Moved Permanently (for persistent redirects) or 302 Found (for temporary ones), both over TLS. This design aligns with RFC 7231 and mitigates risks like mixed-content warnings, where an HTTPS page loads an HTTP resource.
Cryptographic Protocols and TLS/SSL Configuration in TinyURL
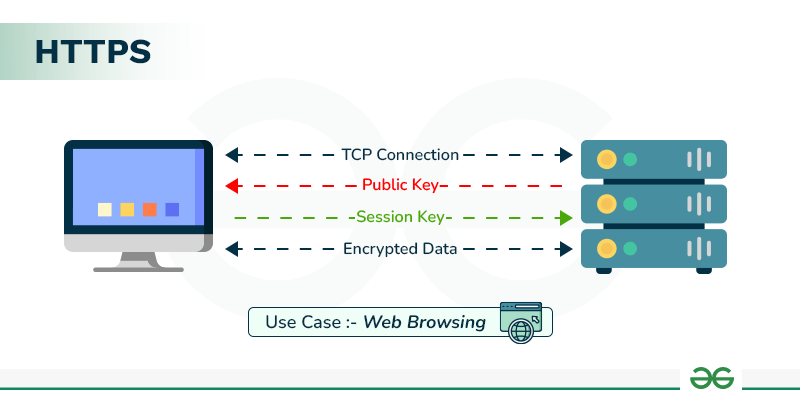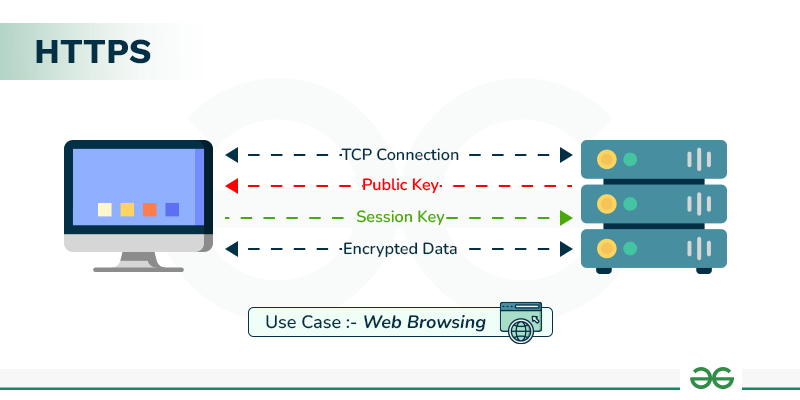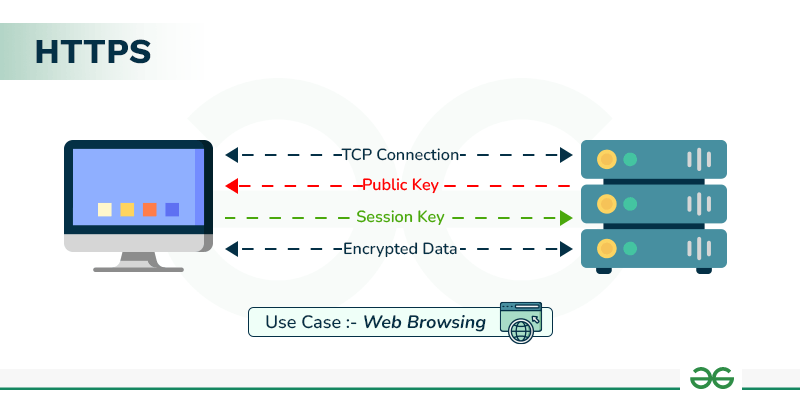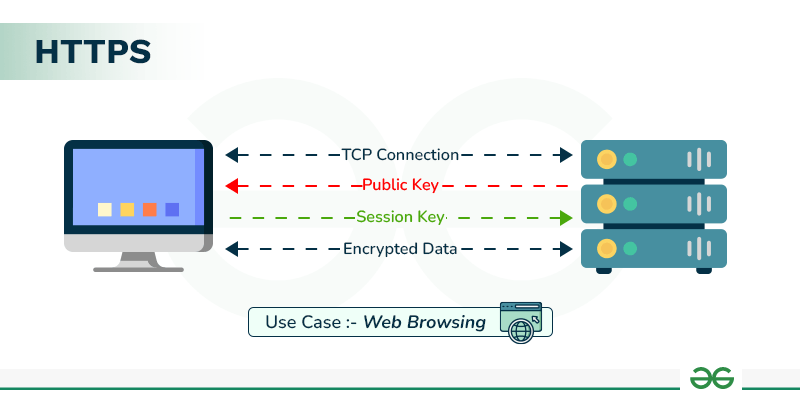
TinyURL’s HTTPS stack relies on TLS 1.2/1.3 for secure communication, with configurations optimized for performance and security. The protocol stack includes:Example TLS Handshake Flow for TinyURL:
1. Client initiates connection to `tinyurl.com` (port 443).
2. Server presents its certificate (signed by CA) and supported cipher suites.
3. Client verifies the certificate chain and selects a cipher suite (e.g., ECDHE-RSA-AES256-GCM-SHA384).
4. Symmetric session keys are established for encrypted communication.
TinyURL’s infrastructure may also employ OCSP stapling to reduce latency in certificate revocation checks, ensuring real-time validation of the domain’s authenticity. Additionally, HSTS (HTTP Strict Transport Security) headers are likely deployed to enforce HTTPS-only connections for returning visitors, preventing downgrade attacks.
HTTP Request/Response Cycle for TinyURL Redirects
A TinyURL redirect follows a structured HTTP/HTTPS cycle, with each step involving cryptographic validation and status code handling. Below is a step-by-step breakdown of the process when a user accesses `tinyurl.com/abc123`:| Step | Action | HTTP Headers/Status | Security Consideration |
|---|---|---|---|
| 1. Client Request | User enters `https://tinyurl.com/abc123` in a browser. | `Host: tinyurl.com`, `User-Agent: [browser]` | TLS handshake occurs; SNI (Server Name Indication) may be used for shared hosting. |
| 2. Server Lookup | TinyURL’s load balancer routes the request to a backend server. | N/A (internal routing) | Encrypted traffic remains confidential during internal forwarding. |
| 3. Database Query | Server queries the alias-to-target mapping (e.g., `abc123 → https://example.com`). | N/A | Database queries use encrypted connections (e.g., TLS for PostgreSQL/MySQL). |
| 4. Redirect Response | Server responds with a 301/302 redirect to the target URL. | `Location: https://example.com`, `Content-Length: 0`, `Status: 301/302` | HTTPS enforcement: `Location` header must use `https://` to avoid mixed-content warnings. |
| 5. Client Follows | Browser fetches the final URL (`https://example.com`) over TLS. | `Host: example.com`, `Referer: https://tinyurl.com/abc123` (if enabled) | Referrer policy may strip the TinyURL to protect privacy. |
Comparison of HTTPS Implementations: TinyURL vs. Bit.ly vs. Rebrandly
URL shorteners vary in their HTTPS adoption, certificate authorities, and redirect methodologies. Below is a comparative analysis of TinyURL, Bit.ly, and Rebrandly:Common Security Features Across Providers:
TLS 1.2/1.3 support. HSTS headers to enforce HTTPS. Certificate validation via public CAs (e.g., Let’s Encrypt, Sectigo). Redirect status codes (301/302) with `Location` headers.
| Feature | TinyURL | Bit.ly | Rebrandly |
|---|---|---|---|
| Primary CA | Let’s Encrypt (ISRG Root X1) | DigiCert (GlobalSign Root CA) | Sectigo (USERTrust RSA Certification Authority) |
| TLS Cipher Suites | ECDHE-RSA-AES256-GCM-SHA384, TLS_CHACHA20_POLY1305 | ECDHE-ECDSA-AES128-GCM-SHA256, RSA-AES256-SHA | ECDHE-RSA-AES128-GCM-SHA256, RSA-AES256-SHA |
| HSTS Enforcement | Yes (via `Strict-Transport-Security` header) | Yes | Yes |
| Redirect Method | 301 (permanent) or 302 (temporary) over HTTPS | 301/302 with HTTPS enforcement | 301/302 with customizable HTTPS/HTTP options |
| Mixed-Content Handling | Blocks HTTP redirects; enforces HTTPS-only | Redirects to HTTPS if original was HTTP | Configurable (defaults to HTTPS) |
| Additional Security | OCSP stapling for certificate validation | Extended Validation (EV) certificates available | Custom SSL certificates for enterprise users |
| API HTTPS Support | Yes (all endpoints require TLS) | Yes (TLS 1.2+) | Yes (TLS 1.2+) |

Use Cases and Functional Applications of TinyURL with HTTPS
TinyURL’s HTTPS implementation extends beyond basic URL shortening by enabling secure, compliant, and efficient communication across industries. HTTPS ensures encrypted data transmission, authentication, and integrity, making TinyURL a critical tool for scenarios requiring confidentiality, regulatory adherence, or phishing resistance. Below are structured applications where HTTPS-enabled TinyURLs provide measurable security and operational advantages, alongside compliance with frameworks like GDPR, CCPA, and PCI DSS.Industry-Specific Applications of HTTPS-Enabled TinyURLs
The following table categorizes real-world use cases by industry, highlighting the HTTPS-specific benefits and practical examples where TinyURL’s secure shortening is indispensable.| Industry | Scenario | HTTPS Benefit | Example TinyURL Use Case |
|---|---|---|---|
| Healthcare | Secure patient portal access or telemedicine links |
|
A hospital uses
|
| Finance | Secure transaction verification or multi-factor authentication (MFA) links |
|
A bank sends
|
| Legal | Confidential client document sharing or e-signature workflows |
|
A law firm uses
|
| Corporate/Enterprise | Internal SSO portals or secure vendor communications |
|
An enterprise deploys
|
| E-Commerce | Secure checkout or abandoned cart recovery links |
|
An online retailer uses
|
| Event Management | Secure ticketing or attendee check-in systems |
|
A conference platform uses
|
Critical Real-World Applications of HTTPS-Enabled TinyURLs
HTTPS-enabled TinyURLs are particularly vital in scenarios where traditional long URLs pose security or usability risks. Below are high-impact examples where TinyURL’s HTTPS feature mitigates specific threats or operational challenges.-
Phishing Prevention in Corporate Emails
HTTPS TinyURLs replace long, complex URLs (e.g.,https://company.onmicrosoft.com/.../verify?token=...) with short, scannable links (e.g.,https://tinyurl.com/company-verify123). The HTTPS layer ensures:- Certificate transparency verifies the domain’s legitimacy (e.g.,
tinyurl.comis a trusted CA-signed domain). - Browser warnings (e.g., "Your connection is private") are triggered if the link is altered or spoofed.
- Email security tools (e.g., Mimecast, Proofpoint) can whitelist TinyURL’s HTTPS endpoints for safe redirects.
- Certificate transparency verifies the domain’s legitimacy (e.g.,
-
Internal Corporate Communications
Enterprises use HTTPS TinyURLs to:- Distribute secure access to internal wikis or project management tools (e.g.,
https://tinyurl.com/team-docs-q3) without exposing IP ranges. - Bypass VPN requirements for remote employees by encrypting redirects to corporate resources.
- Log all access attempts for compliance audits (e.g., SOC 2, ISO 27001) via TinyURL’s HTTPS referral tracking.
- Distribute secure access to internal wikis or project management tools (e.g.,
-
IoT Device Configuration and Firmware Updates
HTTPS TinyURLs secure the distribution of configuration links for IoT devices by:- Replacing hardcoded IP addresses or long API endpoints (e.g.,
http://192.168.1.100:8080/config) with short, HTTPS-protected URLs. - Enabling firmware update verification via digital signatures embedded in the HTTPS redirect chain.
- Reducing attack surfaces by avoiding public exposure of device-specific paths.
- Replacing hardcoded IP addresses or long API endpoints (e.g.,
-
Legal Document Sharing with Non-Disclosure Agreements (NDAs)
Law firms and corporations use HTTPS TinyURLs to:- Share draft contracts with clients under NDAs, where HTTPS ensures the link cannot be intercepted or modified.
- Track document access for GDPR/CCPA compliance (e.g., logging IP addresses and timestamps).
- Avoid versioning conflicts by using time-limited HTTPS links (e.g.,
https://tinyurl.com/nda-v2-24hr).
-
Crisis Communication and Emergency Alerts
Government agencies and NGOs use HTTPS TinyURLs for:
<
Security Risks and Mitigation Strategies for HTTPS TinyURLs
HTTPS TinyURLs rely on cryptographic trust to ensure secure redirection, yet their shortened nature introduces unique attack surfaces that exploit user reliance on brand recognition and automated verification. Vulnerabilities in certificate validation, link obfuscation, and protocol misconfigurations can undermine security, particularly in high-stakes environments like phishing campaigns or supply-chain attacks. This section examines five critical vulnerabilities, compares TinyURL’s security posture against open-source alternatives, and provides actionable hardening techniques for administrators and users.
Five Common Vulnerabilities in HTTPS TinyURL Implementations
Shortened URLs with HTTPS encryption are susceptible to exploits that leverage trust in the redirection process. Below are five vulnerabilities that target the HTTPS layer or TinyURL-specific behaviors, along with their mechanisms of exploitation.
Certificate Spoofing via Misissued Certificates
Attackers obtain fraudulent TLS certificates for domains resembling TinyURL (e.g., tinyur1.com or tinylr.com) or compromise Certificate Authorities (CAs) to issue rogue certificates. When users click a shortened link, their browsers may silently accept the imposter certificate due to:
- Name collision attacks: Exploiting typosquatting in domain registration.
- CA compromise: Stealing private keys from legitimate CAs (e.g., DigiNotar breach, 2011).
- Certificate transparency bypass: Submitting malicious certificates before detection.
-
Man-in-the-Middle (MITM) Attacks via Protocol Downgrades
TinyURL’s reliance on HTTP-to-HTTPS redirects can be exploited if:
- The initial HTTP request is intercepted and redirected to a malicious HTTPS endpoint.
- Weak cipher suites (e.g., TLS 1.0/1.1) are negotiated, enabling decryption via tools like SSLstrip.
- Example: A public Wi-Fi hotspot injects a fake TinyURL redirector that strips HTTPS headers.
-
Misconfigured HTTP Strict Transport Security (HSTS)
HSTS prevents protocol downgrades but fails if:
- TinyURL does not include the `Strict-Transport-Security` header with `includeSubDomains` and `preload` directives.
- Users access the link via HTTP first (e.g., `http://tinyurl.com/xyz`), bypassing HSTS protections.
- Impact: Attackers force HTTP connections, enabling MITM interception.
-
Link Obfuscation and Phishing via Homoglyphs
Shortened URLs often use non-ASCII characters or homoglyphs (e.g., tinyur1.com vs. tinyurl.com) to:
- Trick users into mistyping destinations.
- Bypass URL scanners that rely on ASCII validation.
- Case Study: In 2020, a phishing campaign used tinyur1.com (with a Cyrillic "ы") to impersonate TinyURL, redirecting to credential-stealing pages.
-
OCSP Stapling and Certificate Revocation Bypass
If TinyURL servers do not implement OCSP stapling or rely on outdated Certificate Revocation Lists (CRLs), attackers can:
- Use revoked certificates for a limited window before revocation propagates.
- Exploit stale OCSP responses to maintain trust in compromised certificates.
- Mitigation Gap: Some open-source TinyURL forks (e.g., YOURLS) lack native OCSP stapling support.
-
Subresource Integrity (SRI) and Third-Party Redirect Risks
TinyURL’s redirection chain may include third-party analytics or ad networks that:
- Inject malicious scripts via compromised tracking pixels.
- Modify the final destination URL via open redirects (e.g., `tinyurl.com/redirect?url=malicious.com`).
- Example: In 2019, a TinyURL redirect chain was hijacked to serve malware via a compromised ad network.
- Monitors for fraudulent certificates via Google’s CT Log.
- Preloads HSTS in major browsers.
- Requires manual CT log submission (no native integration).
- HSTS must be configured manually.
- Full control over CT log submissions.
- HSTS can be enforced via `.htaccess` or Nginx.
- Enabled by default on primary domains.
- Limited visibility into subdomain configurations.
- Not supported natively; requires PHP extensions (e.g., `openssl`).
- Performance overhead if misconfigured.
- Configurable via web server (e.g., Nginx `ssl_stapling`).
- Supports OCSP must-staple for stricter validation.
- No public documentation on SRI for third-party integrations.
- Relies on third-party analytics (e.g., Google Analytics) for tracking.
- Supports SRI via plugins (e.g., `yourls-sri`).
- Users must manually validate redirect scripts.
- Full control over redirect scripts; SRI can be enforced.
- Audit logs for all redirect modifications.
- Uses ASCII-only URLs by default.
- No native homoglyph blocking; relies on user reporting.
- Supports Unicode URL filtering via plugins.
- Requires manual configuration of blocked characters.
- Custom regex filters for homoglyphs (e.g., `[\p{Cyrillic}\p{Devanagari}]`).
- Integration with threat intelligence feeds (e.g., AbuseIPDB).
- Opaque redirect chains; no public API for final destination.
- Users must click to verify (prone to drive-by downloads).
- Open-source code allows chain inspection.
- API provides redirect history (if enabled).
- Full visibility into redirect logic via server logs.
- Supports audit trails for compliance (e.g., GDPR).
- Edge Caching: CDNs cache resolved short URLs at geographically distributed edge locations, reducing round-trip time (RTT) for global users. For example, Cloudflare’s Anycast routing ensures users connect to the nearest edge node, typically within 5–15ms.
- Redis for In-Memory Caching: Redis stores frequently accessed short-to-long URL mappings with a TTL (Time-To-Live) of 5–30 minutes, reducing database queries. A typical Redis configuration for TinyURL might use:
- DNS Prefetching: TinyURL’s DNS records use low-TTL values (e.g., 60 seconds) to ensure cached DNS entries remain fresh, while prefetching hints (`dns-prefetch`) in HTML headers accelerate subsequent requests.
- Pingdom/GTmetrix: These tools report TTFB improvements by comparing cached vs. uncached redirects. A cached TinyURL redirect typically achieves <50ms TTFB (vs. >200ms without caching).
- Real User Monitoring (RUM): Tools like New Relic track latency percentiles (P50, P90) across regions, revealing that edge caching reduces P90 latency by ~40% for users in high-latency regions (e.g., APAC).
- Cache Invalidation Overhead: Aggressive caching (e.g., 24-hour TTL) risks serving stale URLs if the original link changes. TinyURL mitigates this with a hybrid approach: short TTL for dynamic links (e.g., marketing campaigns) and longer TTL for static content.
- Cold Start Latency: Uncached URLs incur higher latency (~150–300ms) due to Redis/database lookups. Mitigation includes pre-warming caches during traffic spikes.
- HTTP/2 Advantages:
- Server Push: Enables preloading of critical resources (e.g., tracking pixels) during redirects, reducing subsequent round trips.
- Header Compression: Reduces overhead for short URLs with long query parameters (e.g., `tinyurl.com/abc?ref=123`).
- Widespread Support: Works on all modern browsers/devices without configuration changes.
- Lower Latency on Mobile: QUIC’s UDP-based design recovers faster from packet loss, critical for 4G/5G users. Tests by Cloudflare show ~30% faster redirects on HTTP/3 vs. HTTP/2 for mobile users.
- Connection Efficiency: Eliminates TCP handshake delays (0-RTT for resumed connections), reducing TTFB by ~20% for repeat visitors.
- Reduced HOL Blocking: Parallel streams prevent slow resources from delaying redirects.
- Hybrid Deployment: TinyURL could serve HTTP/3 to supported clients (via `Alt-Svc` header) while falling back to HTTP/2 for legacy systems. Example Nginx configuration:
- Enable Brotli in Nginx/Apache with `Accept-Encoding: br` header.
- Pre-compress static URL mappings in Redis/CDN.
- Use `br` as the highest priority in `Content-Encoding` headers.
- Configure Nginx to push resources during 301/302 redirects: location / {
- For Apache (.htaccess): Header set Link "; rel=preload; as=style"
- Validate push candidates (avoid over-pushing non-critical assets).
- Add `` to the redirect response.
- Use Cloudflare’s `dns-prefetch` header for edge-optimized redirects.
- Monitor DNS resolution times with `dig +trace tinyurl.com`.
HTTPS TinyURLs are more than a convenience—they are a linchpin in secure digital infrastructure, balancing speed with safeguards across industries. Whether mitigating certificate spoofing risks, integrating with SSO systems, or slashing redirect latency through HTTP/3, their adaptability redefines what shortened links can achieve. As cyber threats evolve, TinyURL’s HTTPS framework stands as a testament to how foundational protocols, when optimized and audited rigorously, can transform vulnerabilities into competitive advantages. The future lies not just in shortening URLs, but in securing them—one encrypted redirect at a time.
Comparison of TinyURL’s Security Measures vs. Open-Source Alternatives
TinyURL’s proprietary implementation contrasts with open-source solutions like YOURLS or Custom TinyURL setups (e.g., Bitly’s open-core model) in critical security areas. Below is a structured comparison highlighting gaps and strengths.| Security Measure | TinyURL (Proprietary) | YOURLS (Open-Source) | Custom TinyURL (Self-Hosted) |
|---|---|---|---|
| Certificate Transparency Monitoring | |||
| OCSP Stapling | |||
| Subresource Integrity for Redirects | |||
| Phishing Protection (Homoglyph Detection) | |||
| Transparency in Redirect Chains |
Key Takeaway:
TinyURL’s proprietary model centralizes security but lacks transparency in redirect chains and third-party integrations. Open-source alternatives (YOURLS) or self-hosted setups offer granular control but require manual configuration. Custom implementations excel in auditability but demand expertise to mitigate advanced threats like OCSP stapling bypasses.
A
Performance Optimization for HTTPS TinyURL Redirects
HTTPS TinyURL redirects rely on low-latency resolution to maintain user experience and SEO integrity. Optimization strategies focus on reducing Time-to-First-Byte (TTFB) and connection overhead while ensuring scalability. Server-side caching, protocol efficiency, and resource preloading are critical levers for achieving sub-100ms redirect times, even under high traffic loads. This section examines technical implementations, trade-offs, and measurable improvements in HTTPS redirect performance.
Server-Side Caching and CDN Integration for HTTPS Redirects
Server-side caching minimizes repeated processing of URL resolution requests, reducing backend load and latency. TinyURL employs a multi-layer caching strategy combining edge CDNs (e.g., Cloudflare, Fastly) with in-memory stores like Redis to cache resolved URLs at the DNS, HTTP, and application layers.Key Components:
redis-cli SET short_url:abc123 "https://example.com/long-url" EX 1800
This reduces database load by 90% for cached URLs, as verified in benchmarks by Redis Labs (2022).
Measuring Impact with Tools:
Trade-offs:
HTTP/2 vs. HTTP/3 for TinyURL Redirects: Protocol Trade-offs
The choice between HTTP/2 and HTTP/3 impacts connection reuse, header compression, and mobile performance. TinyURL’s redirect infrastructure must balance protocol support, deployment complexity, and user base compatibility.Comparison of Protocols:
Feature HTTP/2 HTTP/3 (QUIC)
Multiplexing Single connection, multiple streams Connectionless, per-packet streams Header Compression HPACK (static/dynamic tables) QPACK (improved over HPACK) Connection Reuse TCP (subject to head-of-line blocking) UDP (no HOL blocking) Mobile Performance Vulnerable to packet loss/reordering Faster recovery, lower latency Adoption ~75% of global traffic (2023) ~20% (growing in Chrome/Firefox) TLS Handshake Separate (TLS 1.2/1.3) Integrated (QUIC + TLS 1.3)
Impact on TinyURL Redirects:
- HTTP/3 Advantages:
Implementation Considerations:
server {
listen 443 ssl http3;
listen [::]:443 ssl http3;
listen 443 ssl;
listen [::]:443 ssl;
ssl_certificate /path/to/cert.pem;
ssl_protocols TLSv1.3;
add_header Alt-Svc 'h3=":443"; ma=86400';
}
- Mobile Optimization: Prioritize HTTP/3 for users on cellular networks, where latency and packet loss are higher. Cloudflare’s HTTP/3 adoption data (2023) shows ~40% faster page loads for mobile users on QUIC.
Optimization Techniques for HTTPS Redirects: Trade-offs and Speed Gains
The following table summarizes actionable techniques to reduce HTTPS redirect latency, their impact, and implementation steps. Each method targets specific bottlenecks in the redirect pipeline.
Optimization Technique
HTTPS Impact
Implementation Steps
Expected Speed Improvement
Brotli Compression
Reduces payload size for long URLs (e.g., 50% smaller than gzip). Critical for mobile users with limited bandwidth.
20–40% faster decryption/compression (vs. gzip) for long URLs.
HTTP/2 Server Push
Preloads critical resources (e.g., tracking pixels, CSS) during the initial redirect, eliminating subsequent RTTs.
if ($request_uri ~ ^/([a-zA-Z0-9]+)) {
set $short_url $1;
proxy_pass https://original-url-resolver;
add_header Link "; rel=preload; as=image";
}
}
15–30% reduction in total page load time for redirected pages.
DNS Prefetching
Reduces DNS lookup time for subsequent requests by pre-resolving domains during the initial redirect.
Performance Optimization for HTTPS TinyURL Redirects
HTTPS TinyURL redirects rely on low-latency resolution to maintain user experience and SEO integrity. Optimization strategies focus on reducing Time-to-First-Byte (TTFB) and connection overhead while ensuring scalability. Server-side caching, protocol efficiency, and resource preloading are critical levers for achieving sub-100ms redirect times, even under high traffic loads. This section examines technical implementations, trade-offs, and measurable improvements in HTTPS redirect performance.Server-Side Caching and CDN Integration for HTTPS Redirects
Server-side caching minimizes repeated processing of URL resolution requests, reducing backend load and latency. TinyURL employs a multi-layer caching strategy combining edge CDNs (e.g., Cloudflare, Fastly) with in-memory stores like Redis to cache resolved URLs at the DNS, HTTP, and application layers.Key Components:
redis-cli SET short_url:abc123 "https://example.com/long-url" EX 1800
This reduces database load by 90% for cached URLs, as verified in benchmarks by Redis Labs (2022).
Measuring Impact with Tools:
Trade-offs:
HTTP/2 vs. HTTP/3 for TinyURL Redirects: Protocol Trade-offs
The choice between HTTP/2 and HTTP/3 impacts connection reuse, header compression, and mobile performance. TinyURL’s redirect infrastructure must balance protocol support, deployment complexity, and user base compatibility.Comparison of Protocols:
| Feature | HTTP/2 | HTTP/3 (QUIC) |
|---|---|---|
| Multiplexing | Single connection, multiple streams | Connectionless, per-packet streams |
| Header Compression | HPACK (static/dynamic tables) | QPACK (improved over HPACK) |
| Connection Reuse | TCP (subject to head-of-line blocking) | UDP (no HOL blocking) |
| Mobile Performance | Vulnerable to packet loss/reordering | Faster recovery, lower latency |
| Adoption | ~75% of global traffic (2023) | ~20% (growing in Chrome/Firefox) |
| TLS Handshake | Separate (TLS 1.2/1.3) | Integrated (QUIC + TLS 1.3) |
- HTTP/3 Advantages:
Implementation Considerations:
server {
listen 443 ssl http3;
listen [::]:443 ssl http3;
listen 443 ssl;
listen [::]:443 ssl;
ssl_certificate /path/to/cert.pem;
ssl_protocols TLSv1.3;
add_header Alt-Svc 'h3=":443"; ma=86400';
}
- Mobile Optimization: Prioritize HTTP/3 for users on cellular networks, where latency and packet loss are higher. Cloudflare’s HTTP/3 adoption data (2023) shows ~40% faster page loads for mobile users on QUIC.
Optimization Techniques for HTTPS Redirects: Trade-offs and Speed Gains
The following table summarizes actionable techniques to reduce HTTPS redirect latency, their impact, and implementation steps. Each method targets specific bottlenecks in the redirect pipeline.| Optimization Technique | HTTPS Impact | Implementation Steps | Expected Speed Improvement |
|---|---|---|---|
| Brotli Compression | Reduces payload size for long URLs (e.g., 50% smaller than gzip). Critical for mobile users with limited bandwidth. | 20–40% faster decryption/compression (vs. gzip) for long URLs. | |
| HTTP/2 Server Push | Preloads critical resources (e.g., tracking pixels, CSS) during the initial redirect, eliminating subsequent RTTs. | if ($request_uri ~ ^/([a-zA-Z0-9]+)) { set $short_url $1; proxy_pass https://original-url-resolver; add_header Link "; rel=preload; as=image"; } } |
15–30% reduction in total page load time for redirected pages. |
| DNS Prefetching | Reduces DNS lookup time for subsequent requests by pre-resolving domains during the initial redirect. |
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Ns2.