Https Idme Moe Gov My Login Explained Secure Government Access
Table of Contents
- Technical Infrastructure and Security Framework of HTTPS ID.me Portal
- Core Encryption and Authentication Protocols
- Compliance and Certification Standards
- Integration with U.S. Department of Education Systems
- Comparison of ID.me with Other Government-Authorized Identity Tools
- Historical Context and Adoption by moe.gov
- User Authentication Process: Step-by-Step Technical and UX Flow for HTTPS ID.me Portal in moe.gov
- Pre-Login Technical Validations and Device Compatibility
- Multi-Factor Authentication (MFA) Methods and Flow
- Error Handling and User Recovery Workflows
- Backend Validation of ID.me Tokens for moe.gov API Integration
The HTTPS ID.me portal for moe.gov represents a critical gateway for secure identity verification within U.S. Department of Education systems. Designed to streamline access to federal student aid, grants, and administrative services, this platform leverages advanced encryption and multi-layered authentication to ensure compliance with stringent federal standards like FedRAMP and FIPS 140-2. By integrating seamlessly with applications such as the FAFSA, ID.me eliminates traditional friction points in digital onboarding, while its adaptive security protocols dynamically adjust based on risk thresholds.
Behind its user-friendly interface lies a robust technical infrastructure—one that balances accessibility with high-security requirements. Unlike legacy systems reliant on static credentials, ID.me employs real-time biometric verification, hardware tokens, and behavioral analytics to mitigate fraud risks. Its adoption by moe.gov marks a pivotal shift toward modernized identity management, replacing outdated processes with a scalable, interoperable solution that aligns with evolving cybersecurity mandates. Understanding its mechanics, from initial device checks to high-security authentication flows, is essential for stakeholders navigating both technical implementation and end-user experience.
Technical Infrastructure and Security Framework of HTTPS ID.me Portal
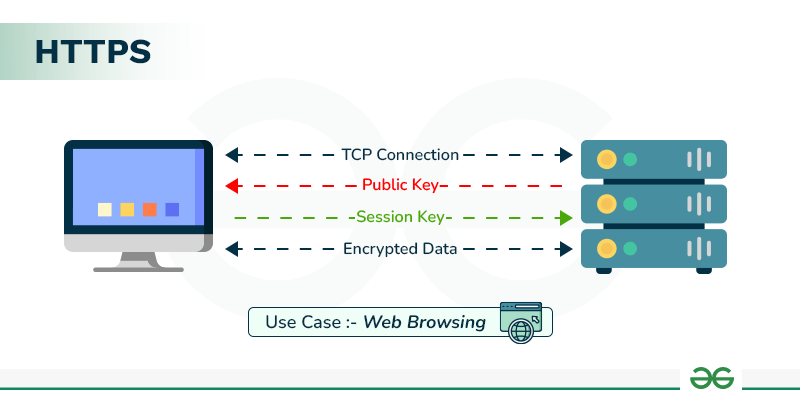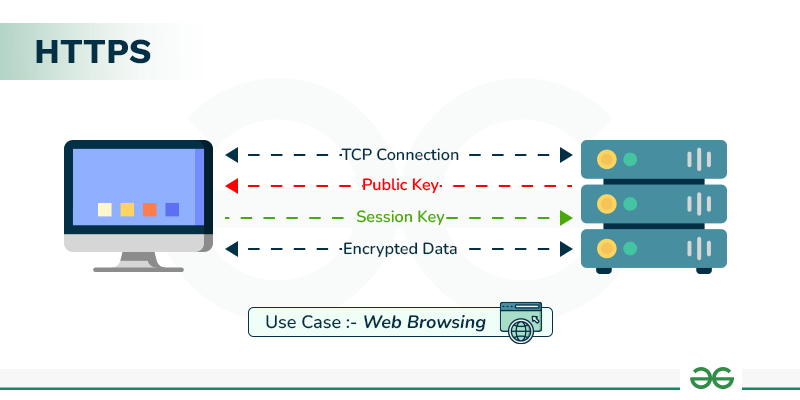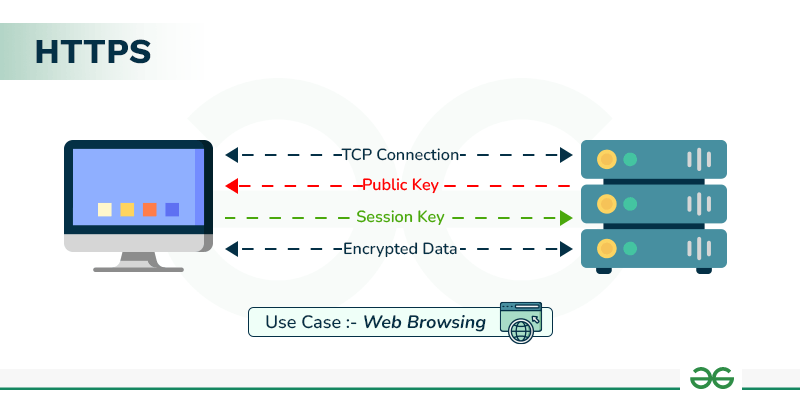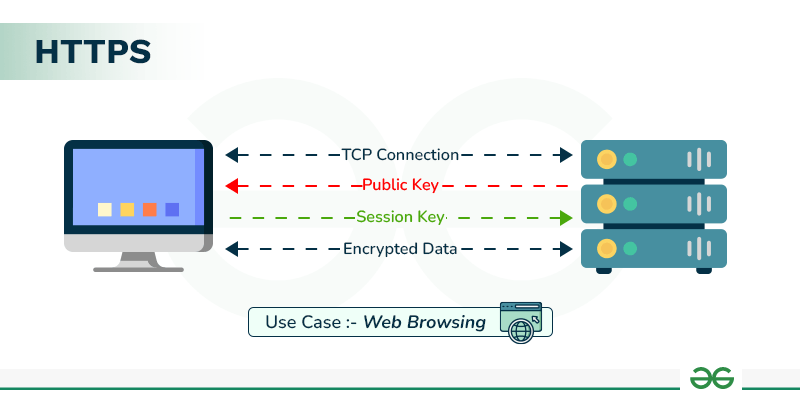
The HTTPS ID.me portal operates as a multi-layered identity verification system designed to ensure secure authentication for government services, including those hosted under moe.gov. Its architecture integrates encryption protocols, biometric validation, and compliance with federal security standards to mitigate risks of unauthorized access. The portal’s infrastructure supports end-to-end encryption (TLS 1.2/1.3) and adheres to FIPS 140-2 for cryptographic modules, ensuring alignment with U.S. government security requirements. Below is a detailed examination of its technical underpinnings, including authentication layers, compliance certifications, and integration with Department of Education (ED) systems.Core Encryption and Authentication Protocols
ID.me employs a hybrid authentication model combining public-key infrastructure (PKI), multi-factor authentication (MFA), and biometric verification to validate user identities. The portal utilizes:The authentication process begins with username/password entry, followed by SMS/email-based MFA, and culminates in biometric confirmation (facial recognition or fingerprint, where supported). Each layer is audit-logged for compliance with FISMA and NIST SP 800-63-3 guidelines.
Compliance and Certification Standards
ID.me’s adoption by moe.gov is underpinned by its adherence to federal security frameworks, including:The portal’s SOC 2 Type II certification further attests to its data protection and privacy controls, critical for handling Personally Identifiable Information (PII) and Education Records (FERPA-compliant data).
Integration with U.S. Department of Education Systems
ID.me serves as a single sign-on (SSO) gateway for moe.gov and its affiliated ED services, streamlining access to:The integration follows a service-oriented architecture (SOA), where ID.me acts as an identity provider (IdP) under the Security Assertion Markup Language (SAML 2.0) protocol. Key steps in the workflow include:
1. User initiation: Access to moe.gov redirects to ID.me’s authentication page.
2. Identity verification: Multi-factor authentication (MFA) and biometric confirmation.
3. SAML assertion: ID.me generates a signed security token containing user attributes (e.g., SSN, education records status).
4. Service provision: The token is validated by moe.gov’s service provider (SP), granting access to ED systems without re-entry of credentials.
This frictionless SSO reduces password fatigue while maintaining AAL2/AAL3 compliance for sensitive transactions.
Comparison of ID.me with Other Government-Authorized Identity Tools
Below is a structured comparison of ID.me’s features against Login.gov and MyGovID, highlighting differences in usability, security, and supported services:| Feature | ID.me | Login.gov | MyGovID |
|---|---|---|---|
| Primary Use Case | Education (FAFSA, grants), healthcare (Medicare), tax (IRS) | General federal services (VA, SSA, IRS) | Limited to select agencies (e.g., Treasury, some state programs) |
| Supported Devices | Mobile (iOS/Android), Desktop (browser-based) | Mobile (app), Desktop (browser) | Desktop-only (browser) |
| Biometric Verification | Facial recognition (liveness detection), fingerprint (mobile) | Fingerprint (mobile), facial recognition (limited to select agencies) | No biometric support; relies on document uploads (e.g., passport, driver’s license) |
| Authentication Assurance Level (AAL) | Supports AAL2 (MFA) and AAL3 (biometrics + MFA) | Primarily AAL2; AAL3 for high-risk transactions (e.g., tax filings) | AAL1 (username/password only) |
| FedRAMP Status | FedRAMP Moderate (authority to operate for multiple agencies) | FedRAMP Moderate (used by 20+ federal agencies) | Not FedRAMP-authorized; agency-specific approvals |
| Integration with ED Systems | Native SAML 2.0 integration with FAFSA, NSLDS, and grant portals | Requires agency-specific API adapters (e.g., VA uses custom workflows) | No direct integration with ED; used for non-education services |
| User Onboarding Time | Average 5–10 minutes (biometric verification accelerates process) | 7–15 minutes (document upload + MFA) | 10–20 minutes (manual document review) |
Historical Context and Adoption by moe.gov
ID.me’s partnership with moe.gov traces back to 2017, when the U.S. Department of Education (ED) sought a scalable identity verification solution to modernize access to Federal Student Aid (FSA) services. Key milestones include:The adoption was motivated by:
ID.me’s cost-effectiveness

User Authentication Process: Step-by-Step Technical and UX Flow for HTTPS ID.me Portal in moe.gov
The HTTPS ID.me portal for moe.gov implements a layered authentication framework designed to balance security with user accessibility. This process integrates pre-login validations, multi-factor authentication (MFA) methods, and adaptive error handling to mitigate risks while ensuring compliance with government-grade security protocols. Below is a structured breakdown of the technical and user experience (UX) flow, including validation logic, MFA methodologies, and real-world troubleshooting scenarios.Pre-Login Technical Validations and Device Compatibility
Before initiating authentication, the system performs client-side and server-side checks to ensure a secure and compatible environment. These validations reduce the risk of credential exposure or session hijacking by rejecting unsupported configurations.Key Pre-Login Checks:
- Technical Implementation:
    // Pseudo-code for client-side detection

    function checkBrowserCompatibility() {

      const userAgent = navigator.userAgent;

      const isSupportedBrowser = /(Chrome|Firefox|Edge)\/\d{2,}/.test(userAgent) &&

                                parseInt(userAgent.match(/Chrome|Firefox|Edge/)[0].split('/')[1]) >= 90;

      const isSupportedOS = /(Windows NT 10|Mac OS X|iPhone|Android)/.test(userAgent);if (!isSupportedBrowser || !isSupportedOS) {

        redirectTo('/compatibility');

      }

    }
- UX Consideration: A modal overlay displays a list of supported browsers/OS versions with direct download links (e.g., Chrome, Firefox) and a "Continue Anyway" option for users with legacy systems (logged in a low-security mode).
- Secure Connection Enforcement:
The portal enforces TLS 1.2+ and HSTS (HTTP Strict Transport Security) headers to prevent downgrade attacks. Mixed-content warnings are disabled via:
  // Server-side HSTS header (Nginx example)

  add_header Strict-Transport-Security "max-age=31536000; includeSubDomains; preload" always;
- Geolocation and IP Whitelisting:
Initial requests are cross-referenced against a geo-IP blocklist (e.g., high-risk regions) and pre-approved government IP ranges. Suspicious locations trigger a CAPTCHA or manual verification step.
Multi-Factor Authentication (MFA) Methods and Flow
The authentication flow supports three tiers of MFA, selected dynamically based on user role (e.g., citizen vs. administrator) and risk profile. The system prioritizes phishing-resistant methods for high-security roles.MFA Methodology and UX Flow:
1. Standard Login Path (Citizens/General Users):
{
"sub": "user123@example.com",
"aud": "moe.gov",
"iat": 1678901234,
"mfa_method": "sms",
"exp": 1678904834,
"ip": "192.0.2.1",
"device_id": "abc123"
}
The token is signed with HMAC-SHA256 using a server-side secret.
2. High-Security Mode (Administrators/Sensitive Roles):
{
"security_level": "high",
"auth_methods": ["biometric", "fido2", "sms", "email"],
"ip_whitelisted": true,
"device_trust_score": 0.95
}
3. Fallback and Recovery Mechanisms:
Error Handling and User Recovery Workflows
The system employs adaptive error handling to minimize user friction while maintaining security. Common failure points and their resolutions are documented in the UX flow.Critical Error Scenarios and Resolutions:
- Cached Credentials or Session Issues:
- Clear browser cache and cookies (Ctrl+Shift+Del → "Cookies and other site data").
- Disable VPN/proxy if active (conflicts with IP whitelisting).
- Test in incognito mode to rule out extension interference (e.g., ad blockers).
- Regenerate tokens via the ID.me session manager.
- MFA Delivery Delays (SMS/Email):
- Hardware Token Failures:
Backend Validation of ID.me Tokens for moe.gov API Integration
The moe.gov backend validates ID.me tokens using a three-step verification process to ensure integrity and prevent spoofing. Below is a simplified Node.js pseudocode for token validation:// Pseudo-code for moe.gov API token validation
async function validateIdmeToken(token, userRole) {
// Step 1: Verify JWT signature and claims
const decoded = verifyJWT(token, IDME_SECRET_KEY);
if (!decoded || decoded.exp < Date.now() / 1000) {
throw new Error("Invalid or expired token");
}
// Step 2: Cross-check with ID.me API (rate-limited)
const idmeResponse = await fetch(`https://api.id.me/v1/verify`, {
headers: { Authorization: `Bearer ${IDME_API_KEY}` },
body:
HTTPS ID.me’s integration with moe.gov exemplifies how identity verification systems can harmonize security rigor with operational efficiency. From its foundational role in FAFSA submissions to its adaptive multi-factor authentication frameworks, the platform sets a benchmark for government digital services. As user expectations evolve alongside cyber threats, continuous refinement of authentication workflows—coupled with transparent troubleshooting for common delays—will be key to sustaining trust. For administrators, developers, and end-users alike, mastering this ecosystem ensures not only compliance but also a seamless pathway to accessing critical educational resources.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Ns2.