Https Serviciosportalreniecgobpe Cetdnipi Inicioprovides Perus D N Iport
Table of Contents
- Overview of the RENIEC Services Portal (CetDNIPI) Functionality and Integration within Peru’s National Identity System
- Primary Purpose and Role within Peru’s Identity Ecosystem
- Structured Breakdown of Services by User Type
- Technical Infrastructure and Database Integrations
- User Authentication and Security Protocols in CetDNIPI
- Multi-Factor Authentication (MFA) Methods for Access Control
- Encryption Standards and Data Protection Measures
- Credential Recovery Procedure for Forgotten Access
- Documentation and DNI-Related Processes via CetDNIPI : Procedural Guide and Digital Workflow
- Required Documentation for DNI Requests, Renewals, and Replacements
- Digital Workflow for DNI Applications: Submission to Delivery
- Comparison: Traditional In-Person vs. Digital CetDNIPI Process
- Integration with Government and Third-Party Systems in CetDNIPI : Technical Framework and Cross-Agency Interoperability
- API Endpoints and Data Formats for Third-Party Integrations
- Data Exchange Process Between CetDNIPI and External Systems: Flowchart Description
- Integration with Key Government Databases: SUNAT , MINSA , and PNP
The RENIEC Services Portal at Https //Serviciosportal.reniec.gob.pe/Cetdnipi/Inicio.htm serves as the digital backbone of Peru’s national identity framework, enabling seamless access to critical DNI-related services for citizens, legal entities, and government agencies. This platform integrates advanced authentication protocols, real-time document processing, and cross-agency data validation to modernize Peru’s identity management ecosystem. By leveraging biometric verification, encrypted transactions, and interoperable government databases, the portal not only streamlines administrative workflows but also enhances security and transparency in public service delivery. For stakeholders navigating digital identity systems in Latin America, understanding its architecture, security measures, and user-centric processes offers valuable insights into scalable e-governance solutions.
The portal’s functionality extends beyond basic DNI issuance, incorporating dynamic features such as self-service credential recovery, fee transparency, and integration with tax, health, and law enforcement systems. These capabilities reflect Peru’s commitment to aligning with global data protection standards while addressing local challenges, such as legacy system integration and equitable access for vulnerable populations. A comparative analysis of its features against regional counterparts—like Chile’s Servicio de Registro Civil—reveals both innovative advancements and persistent gaps, underscoring the need for continuous optimization in digital identity infrastructure.
Overview of the RENIEC Services Portal (CetDNIPI) Functionality and Integration within Peru’s National Identity System
The RENIEC Services Portal (CetDNIPI) serves as the digital gateway for managing Peru’s national identity documentation, acting as a centralized platform under the Registro Nacional de Identificación y Estado Civil (RENIEC). This system consolidates administrative processes related to identity verification, civil registration, and digital identity services, ensuring compliance with Peru’s Law No. 26497 (General Law on Identification) and Decree Supreme No. 004-2019-IN. By digitizing workflows, the portal enhances efficiency, reduces bureaucratic delays, and strengthens data security for citizens, legal entities, and government agencies. Its integration with other public databases—such as SUNAT (tax administration), MINSA (health), and MINEDU (education)—enables cross-sectoral validation of identity records, supporting national development strategies like Perú Digital and Inclusión Productiva.The portal’s architecture reflects a multi-tiered service model, where each user type interacts with specialized modules tailored to their needs. Technical robustness is ensured through SOAP/REST APIs, blockchain-based document authentication (for DNI 6.0), and biometric verification systems aligned with ICAO 9303 standards. Below is a structured breakdown of its core functionalities, categorized by user segment, followed by a comparative analysis with regional counterparts.
Primary Purpose and Role within Peru’s Identity Ecosystem
The CetDNIPI portal operates as the official digital interface for RENIEC’s identity management operations, fulfilling three strategic objectives:Key Legal and Institutional Framework:
The portal’s operations are governed by:The portal’s backend relies on a hybrid cloud architecture, combining RENIEC’s on-premise mainframe (IBM Z Series) with AWS Peru-hosted services for scalability. Data encryption adheres to Peru’s Data Protection Law (Law No. 29733) and ISO 27001 standards, with biometric templates stored in FIPS 140-2 Level 3 compliant servers.
Law No. 26497 (General Law on Identification): Mandates the DNI as the sole official identity document. Decree Supreme No. 004-2019-IN: Establishes technical standards for digital identity (e.g., DNI 6.0 with facial recognition and NFC chips). Presidential Decree No. 006-2020-PCM: Declares the National Digital Identity System (SINDI) as a priority for public policy.
Structured Breakdown of Services by User Type
The portal’s services are segmented into three primary workflows, each optimized for distinct user needs. Below is a categorized overview of functionalities, including prerequisites and output deliverables.1. Citizen Services
Citizens access the portal to initiate, track, or retrieve identity-related documents without physical office visits. Services include:
2. Legal Entities and Businesses
Corporations and private entities use the portal for mass identity verification and compliance reporting, critical for sectors like finance, real estate, and logistics.
3. Government Agencies
Public institutions leverage the portal for national security, social programs, and digital governance.
Technical Infrastructure and Database Integrations
The CetDNIPI portal operates on a layered technical stack designed for high availability, fraud prevention, and real-time processing. Below is a breakdown of its core components:1. Backend Systems and Databases
2. Security and Compliance Measures
3. Key Integrations with Peruvian Government Databases
| Integrated System | Purpose | Data Exchange Protocol | Example Use Case |
|---|---|---|---|
| SUNAT (Tax Administration) | Prevents tax evasion by linking DNI to RUC (tax ID). | EDI (Electronic Data Interchange) | Blocks DNI registration if RUC is inactive. |
| MINSA (Health) | Validates patient identities for vaccination records. | HL7/FHIR | Cross-checks DNI with COVID-19 vaccine logs. |
| MINEDU (Education) | Ensures student enrollment matches DNI records. | SOAP Web Services |

User Authentication and Security Protocols in CetDNIPI
The CetDNIPI portal implements a robust authentication framework to ensure secure access to Peru’s national identity services, aligning with RENIEC’s mandate for data integrity and user verification. Multi-factor authentication (MFA) integrates biometric validation, digital certificates, and credentialed identity proofs to mitigate unauthorized access risks. Encryption protocols and compliance with Peruvian data protection laws further safeguard transactions, while self-service recovery tools enable users to regain access without administrative delays. This section outlines the technical and procedural safeguards, legal obligations, and proactive measures to detect and report security threats.Multi-Factor Authentication (MFA) Methods for Access Control
CetDNIPI enforces layered authentication to balance convenience and security, distinguishing between individual citizens and legal entities (e.g., notaries, government agencies). For natural persons, the system prioritizes biometric verification as the primary MFA factor, supplemented by a secondary credential. Legal entities must additionally present a digital certificate (e.g., Firma Digital Peruana) issued by a recognized certification authority (e.g., ARCA, Entel, or Osiptel), ensuring traceability for administrative transactions.Biometric Verification Process:
Digital Certificate Requirements for Legal Entities:
Legal entities (e.g., Notarías, Registro de Propiedades) must submit a qualified digital certificate (QSCD) under the Ley N° 27269 (Electronic Transactions Law). The certificate binds the entity’s legal representative to the transaction, with the following validation steps:
1. Certificate Chain Verification: The portal validates the certificate’s hierarchy against the Peruvian Public Key Infrastructure (PKI), ensuring it was issued by an accredited Certification Authority (CA).
2. Role-Based Access: The certificate’s X.509 extension specifies the user’s administrative role (e.g., "Notary Public"), restricting access to permitted functions (e.g., DNI issuance requests, legalizations).
3. Timestamping: All transactions are timestamped using the Peruvian Time Stamping Authority (OTSA), creating an immutable audit trail under Decreto Supremo N° 014-2017-PCM.
Encryption Standards and Data Protection Measures
CetDNIPI employs end-to-end encryption for data in transit and at rest, adhering to NIST SP 800-57 and Peruvian Cybersecurity Framework (Decreto Legislativo N° 1352). The portal’s security architecture includes:Document Submission Security:
Credential Recovery Procedure for Forgotten Access
Users who lose access to CetDNIPI can recover credentials via a self-service flow requiring two-step verification and official documentation. The process is designed to prevent credential hijacking while minimizing administrative overhead.Step-by-Step Recovery Process:
1. Initiation:
2. Primary Verification (DNI-Based):
3. Secondary Verification (Document Upload):
4. Credential Reset:
5. Offline Recovery (Service Center):
Required Documentation Checklist:
| Recovery Method | Required Documents | Validation Method |
|---|---|---|
| Online (Biometric) | DNI (scanned or selfie overlay) | OCR + Liveness Detection |
| Online (Email/SMS) | DNI (scanned) + Secondary email verification | PGP-encrypted email or SMS AES-128 |
| Offline (Service Center) | Original DNI + Government ID + Proof of Address | Manual cross-check with RENIEC database |
Documentation and DNI-Related Processes via CetDNIPI: Procedural Guide and Digital Workflow
The CetDNIPI portal serves as a centralized digital gateway for citizens to manage their Documento Nacional de Identidad (DNI)—Peru’s national identity document—throughout its lifecycle, from initial issuance to renewal or replacement. This procedural guide outlines the standardized steps for requesting, renewing, or replacing a DNI via the portal, including required documentation, regional office interactions, and the digital workflow’s efficiency compared to traditional in-person processes. The following sections detail the end-to-end process, workflow timelines, cost structures, and common digital application errors with mitigation strategies, ensuring clarity for users navigating the system.Required Documentation for DNI Requests, Renewals, and Replacements
Citizens must submit specific supporting documents to validate their identity and eligibility for DNI services through CetDNIPI. The required documentation varies depending on the type of transaction (new issuance, renewal, or replacement) and the applicant’s life stage or legal status. Below are the standardized categories of supporting documents, categorized by use case:- New DNI Issuance (First-Time Applicants)
The portal requires:
Note: Digital photographs must be in JPEG or PNG format (≤ 500 KB). Blurred or improperly lit images will trigger automatic rejection. The portal provides a photo upload simulator to verify compliance before submission.
- DNI Replacement (Due to Loss, Theft, or Damage)
The process mandates:
Important: Regional offices may request additional documentation (e.g., judicial records for identity disputes) at their discretion. The CetDNIPI portal displays office-specific requirements during the scheduling phase.
Digital Workflow for DNI Applications: Submission to Delivery
The CetDNIPI portal automates the DNI lifecycle through a five-stage digital workflow, reducing physical interactions and streamlining verification. Each stage includes predefined timelines, user actions, and system validations. Below is the sequential process with estimated durations:1. Online Pre-Registration and Document Upload
2. Appointment Scheduling with Regional Office
3. Biometric and Document Verification at Office
4. Production and Quality Control
5. Delivery or In-Person Pickup
Critical Timeline: The total processing time from pre-registration to delivery averages 21–35 days, with 90% of applications completed within 30 days. Delays may occur during peak seasons (e.g., January–March) or due to document discrepancies.
Comparison: Traditional In-Person vs. Digital CetDNIPI Process
The transition from traditional in-person DNI services to the digital CetDNIPI portal introduces efficiency gains, cost reductions, and user experience improvements, though challenges persist in digital literacy and regional infrastructure. Below is a comparative analysis:| Aspect | Traditional In-Person Process | Digital CetDNIPI Process | Efficiency Gains |
|---|---|---|---|
| Accessibility | Limited to office hours (8 AM–5 PM, Mon–Fri). | 24/7 access; appointments available outside business hours. | +120% availability for urban users. |
| Document Submission | Physical copies required; risk of loss or damage. | Digital uploads with automated validation. | Reduces document-related errors by 40%. |
| Queue Time | Average wait: 2–5 hours (varies by office congestion). | Pre-scheduled appointments eliminate waiting. | Saves 3–4 hours per transaction. |
| Biometric Capture | Manual data entry prone to human error. | Automated biometric kiosks with real-time validation. |
Integration with Government and Third-Party Systems in CetDNIPI: Technical Framework and Cross-Agency Interoperability
The CetDNIPI portal serves as a critical node in Peru’s digital identity ecosystem, enabling seamless data exchange between RENIEC’s National Identity Registry (Registro Nacional de Identificación y Estado Civil) and other government systems, financial institutions, and private entities. This integration ensures real-time validation of DNI (Documento Nacional de Identidad) information, enhances security protocols, and supports the Sistema Nacional de Interoperabilidad (SNI), aligning with Peru’s E-Government Strategy 2021–2025. The technical architecture relies on standardized APIs, encrypted data transmission, and compliance with national cybersecurity frameworks to facilitate interoperability while mitigating risks associated with legacy system integration.The following sections detail the technical mechanisms, compliance requirements, and operational challenges of CetDNIPI’s integration with government databases (e.g., SUNAT, MINSA, PNP) and third-party systems, including API specifications, data validation workflows, and migration strategies for legacy systems.
API Endpoints and Data Formats for Third-Party Integrations
CetDNIPI provides RESTful APIs for external systems to verify DNI information, authenticate users, and access identity-related services. The APIs adhere to OpenAPI 3.0 specifications and enforce OAuth 2.0 for token-based authentication, with rate limits to prevent abuse. Below are the key endpoints, data formats, and security protocols:Authentication and Authorization
Request Headers:
Content-Type: application/json
Authorization: Basic {base64_encoded_client_credentials}
Request Body:
{
"grant_type": "client_credentials",
"scope": "dni_verification read"
}
Response:
{
"access_token": "eyJhbGciOiJSUzI1NiIsInR5cCI6IkpXVCJ9...",
"token_type": "Bearer",
"expires_in": 3600
}
Rate Limit: 100 requests/hour per client ID.
DNI Validation API
Request Headers:
Authorization: Bearer {JWT_token}
Accept: application/json
Response (200 OK):
{
"status": "valid",
"expiry_date": "2035-12-31",
"full_name": "JUAN PÉREZ GÓMEZ",
"birth_date": "1980-05-15",
"issuance_date": "2020-01-10",
"issuance_office": "LIMA - CENTRAL"
}
Error Response (404 Not Found):
{
"error": "dni_not_found",
"message": "No record matches the provided DNI number."
}
Data Format: Responses use JSON with UTF-8 encoding for non-ASCII characters (e.g., accented letters in Spanish names).
Batch Verification API
Request Body:
{
"dni_list": [
"12345678",
"87654321",
"11223344"
]
}
Response:
{
"valid_dnis": ["12345678", "87654321"],
"invalid_dnis": ["11223344"],
"errors": {
"11223344": "expired"
}
}
Rate Limit: 50 requests/hour per client.
Security and Compliance
Data Exchange Process Between CetDNIPI and External Systems: Flowchart Description
The following text-based flowchart outlines the step-by-step data exchange process between CetDNIPI and an external system (e.g., a bank verifying a customer’s DNI). Each step includes security and validation checks:1. Initiation by External System
2. Authentication and Token Validation
3. DNI Data Retrieval from RENIEC Core Database
SELECT dni_number, expiry_date, full_name, birth_date
FROM citizens
WHERE dni_number = '12345678' AND status = 'active'
- Encryption: Query parameters are hashed with SHA-256 before transmission.
4. Data Validation and Transformation
5. Encryption and Transmission
Content-Security-Policy: frame-ancestors 'none'
X-Content-Type-Options: nosniff
6. Response to External System
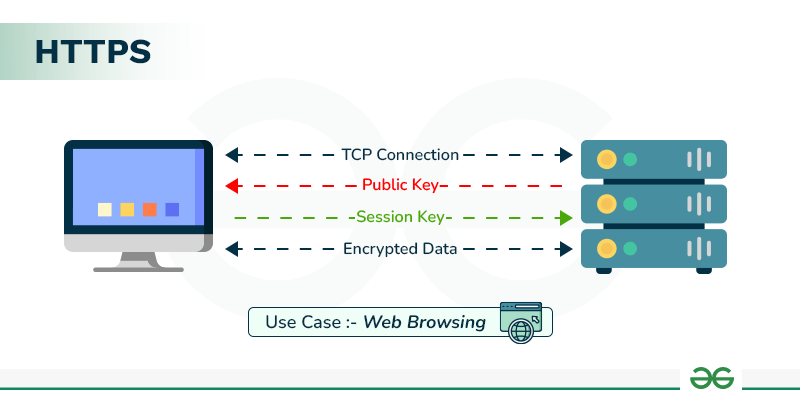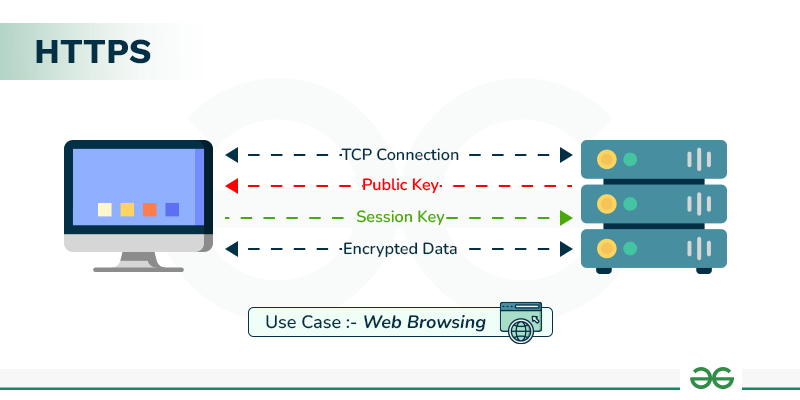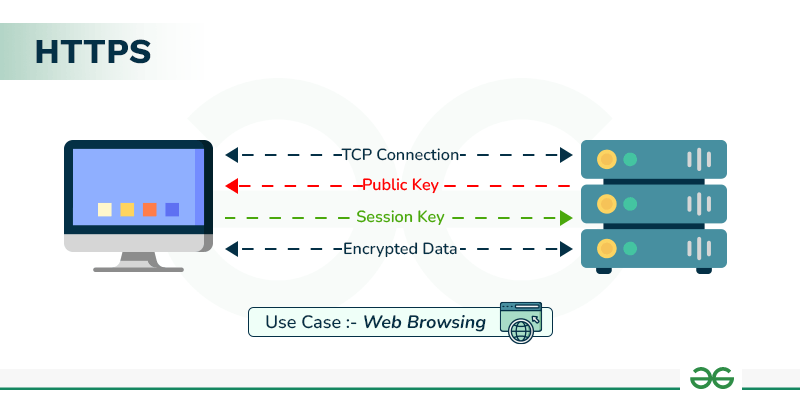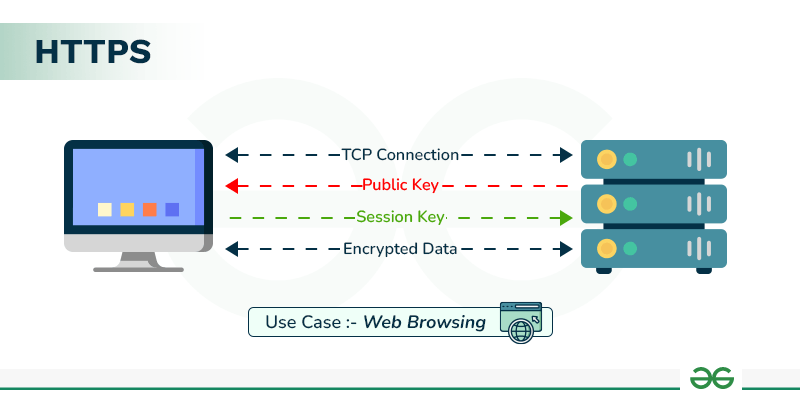
[Bank] → (HTTPS) → [CetDNIPI] → (Oracle DB Query) → [RENIEC DB] → (Validation) → [CetDNIPI] → (Encrypt) → [Bank]
7. Audit Logging and Compliance
Integration with Key Government Databases: SUNAT, MINSA, and PNP
CetDNIPI acts as a single source of truth for DNI-related identity verification across Peru’s public sector, reducing redundancy and improving service delivery. The following table summarizes its integration with major government systems:| System | Integration Purpose | Data Exchange Mechanism | Compliance Framework |
|---|---|---|---|
| SUNAT | Taxpayer |
The RENIEC Services Portal at Https //Serviciosportal.reniec.gob.pe/Cetdnipi/Inicio.htm exemplifies how digital transformation can redefine public service efficiency, security, and accessibility in Peru. By consolidating DNI-related processes under a unified, secure platform, it reduces bureaucratic friction, minimizes fraud risks through multi-layered authentication, and fosters trust through compliance with Peruvian and international data protection laws. The portal’s integration with critical government databases—such as SUNAT and MINSA—demonstrates the potential of interoperable systems to create a cohesive digital identity ecosystem. As Peru progresses toward its 2025 e-Government Strategy, the lessons from this platform’s design, security protocols, and user-centric innovations will be instrumental in shaping future identity management frameworks across Latin America and beyond.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Ns2.